The Evidentiary Foundation for Media Capture
"Your moments, verifiably sealed."
— Making capture events verifiable, not content truth
" As AI-generated imagery becomes indistinguishable from captured media, the ability to verify when, where, and by whom a capture event occurred becomes critical for personal archives, legal evidence, and historical documentation. "
CPP is NOT a content authentication system.
CPP IS a framework for creating verifiable capture records that third parties can independently audit.
"Verify, Don't Trust." — External RFC 3161 TSA anchoring enables independent verifiability.
VeraSnap (B2B)
Evidence-grade capture for legal & journalism
VeraSnap Moments (B2C)
Future-proof family memories
Clear distinction between objective capture data and subjective interpretation
Design Philosophy: "We make capture events verifiable. We do not claim they depict truth."
CPP application scope by priority
Legal Evidence
Evidence-oriented capture records (admissibility is for courts to decide)
Key: RFC 3161 TSA, chain of custody
News / Journalism
Source verification for media
Key: Deletion detection, timestamping
Personal Archives
Family memories with provenance
Key: Long-term verification, ease of use
Insurance Claims
Damage documentation
Key: Location evidence, timestamp evidence
Academic Research
Field data collection
Key: Integrity, reproducibility
Real Estate
Property documentation
Key: Date evidence, completeness
What CPP addresses and what it doesn't
Backdating
Claiming capture occurred at an earlier time
Detectable via: RFC 3161 TSA external timestamp
Tampering
Modifying media after capture
Detectable via: SHA-256 hash chain, digital signature
Cherry-Picking
Deleting unfavorable captures
Detectable after anchoring via: PrevHash event chain and TSA-anchored Merkle batches (events removed before anchoring, or never recorded, are not detectable)
Fabrication
Claiming AI-generated content was captured
Not established by CPP: a capture record shows that a device recorded a capture event; it does not show that the content is not AI-generated (CPP v1.4 depth analysis indicates screen likelihood only)
Scene Staging
Content truth outside scope
Alternative: Human judgment, investigation
Device Compromise
Hardware security out of scope
Alternative: TEE/Secure Enclave (future)
Identity Fraud
Identity verification not claimed
Alternative: External KYC services
Network Interception
Transport security out of scope
Alternative: TLS, certificate pinning
CPP v1.0 event model (superseded). Since CPP v1.1 the specification's event types are INGEST, EXPORT and TOMBSTONE; CPP_SEAL was removed and replaced by batch anchoring.
Media Capture Initiated
Records the capture event with device ID, media hash, and timestamp.
Required Fields:
Cryptographic Seal Applied
Applies cryptographic seal with external timestamp anchor.
Required Fields:
Media Shared (Optional)
Records sharing with verification link for recipients.
Required Fields:
Third-Party Verification (Optional)
Records when third parties verify the capture.
Required Fields:
Cryptographic foundation for verifiable capture records
CPP v1.0 mechanism, removed in CPP v1.1 and shown here for reference only. Since v1.1, removal of an event is detectable through the PrevHash event chain and, after anchoring, against the TSA-anchored Merkle batch. The most recent events, if removed before they are anchored, and captures that were never recorded are not detectable.
// Completeness Invariant Structure CI = { expected_count: n, // Number of events hash_sum: H(E1) ⊕ H(E2) ⊕ ... ⊕ H(En), // XOR of all event hashes first_timestamp: T1, // Earliest event last_timestamp: Tn // Latest event } // Verification Algorithm if len(events) != expected_count: return VIOLATION if XOR(H(events)) != hash_sum: return VIOLATION return VALID
CPP v1.0–v1.1 design (v1.1 §3.2 uses the path /p/{proof_id}); the later change documents up to v1.4 do not restate it. No verification service is currently operated at this address; the SLA and retention figures below are CPP v1.0 design targets, not a service commitment.
https://verify.veritaschain.org/cpp/{verification_code}
SLA
99.95% availability
Retention
50+ years
Recovery
pHash matching
Biometric Attestation at Capture Time
"Who was holding the device when the capture occurred?"
ACE records verifiable evidence that an authentication attempt occurred.
ACE does NOT verify identity.
SUCCESS
Biometric matched enrolled profile
FAILURE
Biometric did not match
TIMEOUT
Auth timed out
CANCELLED
User cancelled auth
NOT_ENROLLED
No biometric enrolled on device
Key Design: Capture proceeds regardless of auth result. Auth failure is recorded, not blocking.
"We record verifiable evidence that authentication was attempted. We store no biometric data."
The Bronze / Silver / Gold levels shown below are from CPP v1.0–v1.1 and are superseded. CPP v1.4 (§8) defines five levels — CPP-BASIC, CPP-TIMESTAMPED, CPP-STANDARD, CPP-ENHANCED and CPP-FULL — and the XOR Completeness Invariant was removed in CPP v1.1. Since v1.1 the required signature algorithm is ES256 (ECDSA P-256); Ed25519 is optional.
Hobbyists, Early Adopters
Use: Personal archives
Self-verifiable only
Families, Prosumers
Use: Long-term memories
Third-party verifiable
Legal, Journalism, Enterprise
Use: Court evidence
Evidence-grade verifiable
Key Principle: External third-party verification (RFC 3161 TSA) is what distinguishes "Provenance Available" from mere self-attestation.
B2B vs B2C positioning
B2B Evidence Tool
"Verifiable evidence generation"
B2C Consumer Application
"Your moments, verifiably sealed"
Pricing intent (design only; not a service commitment): verification links are meant not to expire when a subscription ends. No verification service is operated today.
Complementary positioning with Content Credentials
| Aspect | C2PA | CPP |
|---|---|---|
| Question Answered | "How was this edited?" | "Was this media captured?" |
| Focus | Content provenance | Capture event provenance |
| Scope | Individual assets | Sequential capture records |
| Deletion Detection | Per-asset only | Sequence-level |
| Metaphor | Content passport | Capture flight recorder |
Integration: CPP can embed C2PA manifests while providing additional sequence-level verifiability.
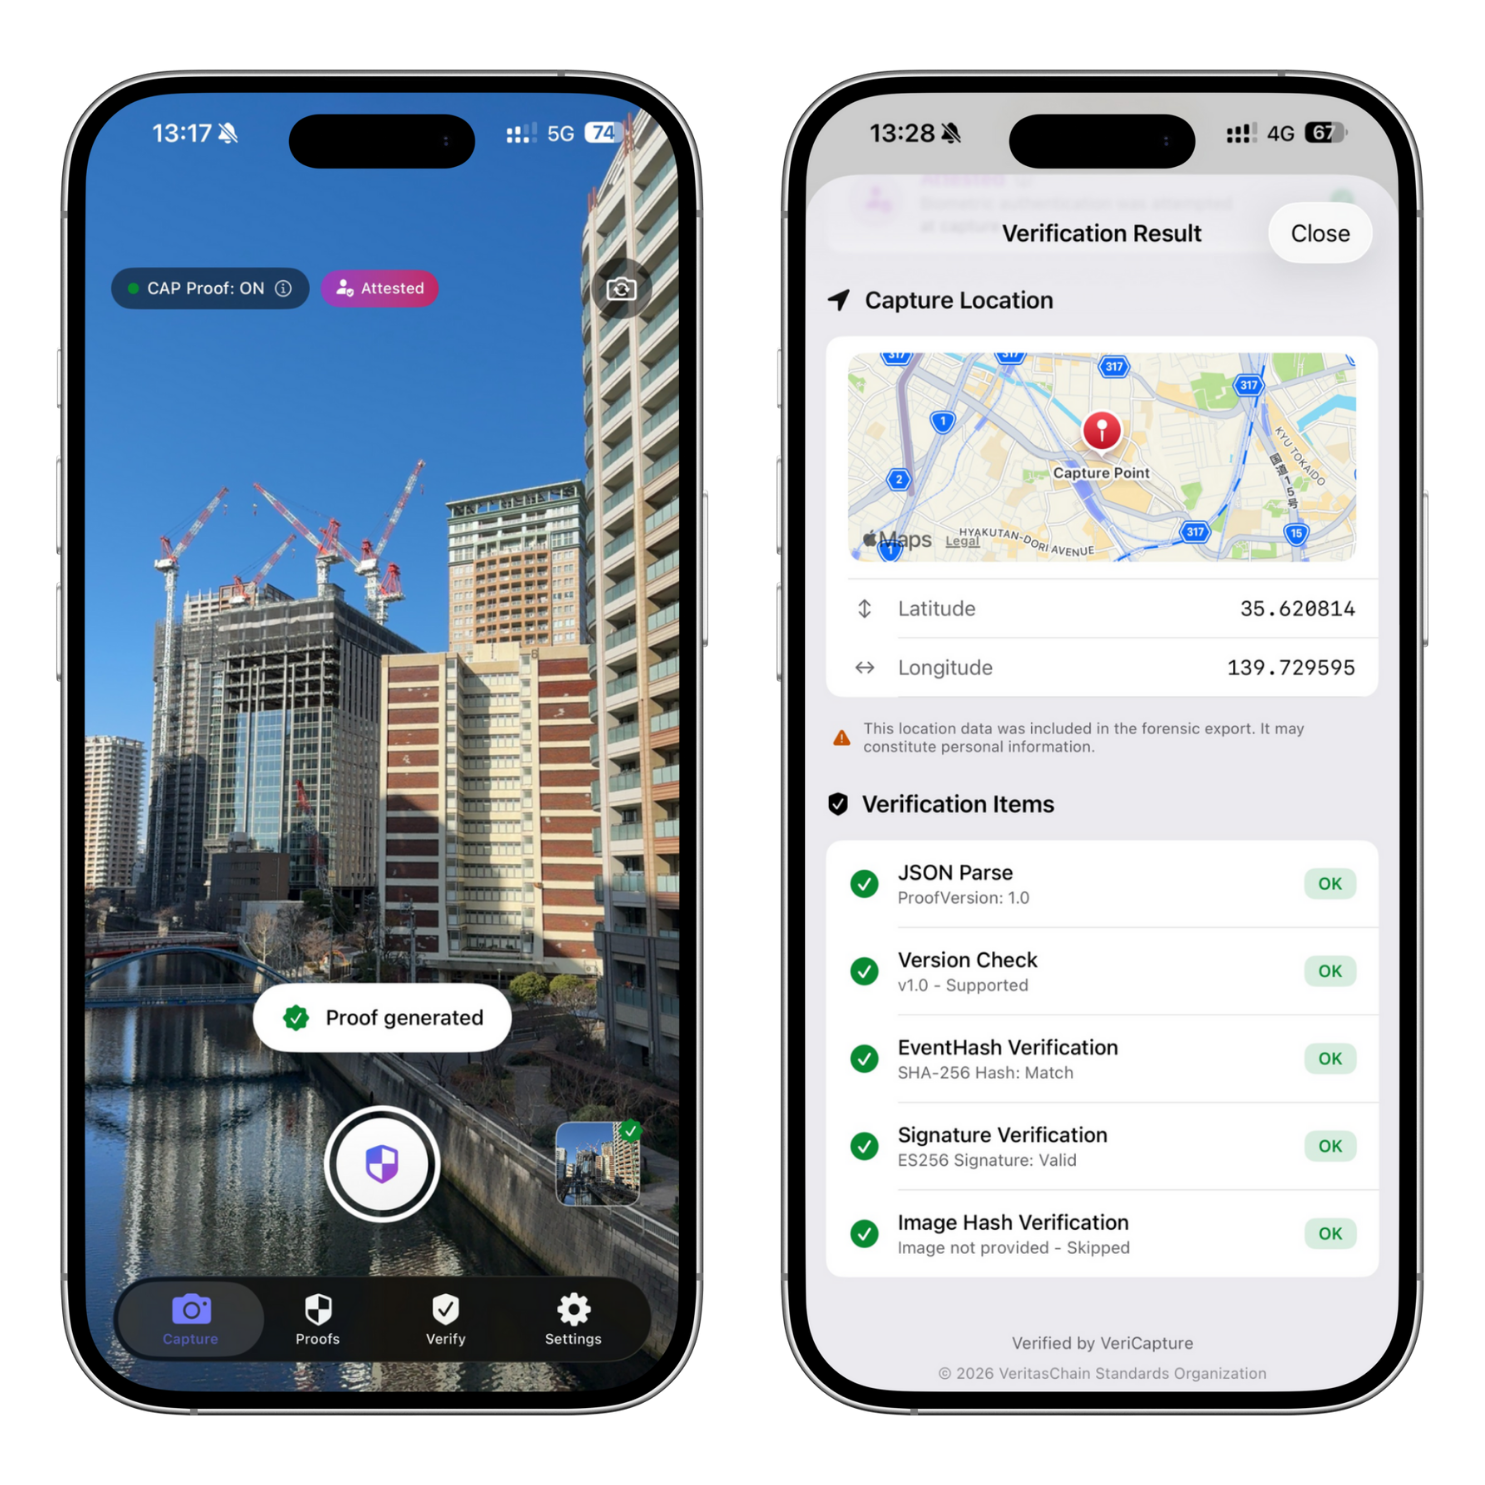
Evidence Generation Tool — first-party implementation of CPP v1.4 by VeritasChain Co., Ltd. (iOS and Android; conformance self-declared)
Evidence Generation Tool
VeraSnap is NOT a camera app. It's a professional evidence generation tool that cryptographically records capture events and data provenance in a tamper-evident manner.
"Verify, Don't Trust."
Important: VeraSnap records capture events — it does NOT verify content truth or legitimacy.
CPP's position in the framework hierarchy
| Aspect | VCP (Finance) | CAP (Content) | CPP (Capture) |
|---|---|---|---|
| Subject | Trading decisions | AI generation decisions | Media capture events |
| Actor | Algorithm/Trader | AI Model/Creator | Device/Photographer |
| Industries | Finance, Trading | Games, Film, AI Platforms | Personal, Legal, News |
| Core Events | SIG/ORD/EXE/CXL | INGEST/TRAIN/GEN/EXPORT | INGEST/EXPORT/TOMBSTONE |
| Time Precision | Nanosecond–Millisecond | Second–Minute | Millisecond–Second |
Join the development of CPP and shape the future of capture provenance
"In an age of AI-generated imagery, verifying that a moment was captured — not created — becomes invaluable."
— VeritasChain Standards Organization
"Your moments, verifiably sealed."
This work is licensed under CC BY 4.0 International
Page content based on CPP Specification v1.0.0 Release Candidate (CPP v1.4 Released 2026-01-29) — Last Updated: 2026-01-18